Q3 2026 · 1,864 PreCVEs Confirmed to Date

Eliminate the
40-Day Disclosure Chasm.

VulNow identifies verified vulnerabilities in your software supply chain an average of 14.4 days before any public advisory exists, before the attacker window opens. We call these Dark Matter Vulnerabilities™: security flaws that exist in production code, invisible to every CVE-based tool but exploitable by attackers.

Q3 2026 PreCVE Confirmation Data
1,864
Confirmed PreCVEs (Cumulative)
14.4d
Avg Lead Time
186d
Max Lead Time (react-router)
870
Packages Across 12 Ecosystems
The Problem

Dark Matter Vulnerabilities™

The fix is in the code. The advisory is not. That gap (hours, days, or months wide) is where breaches happen and where CVE-based tools go blind.

Definition

Dark Matter Vulnerabilities™ are security flaws that exist in open source packages after a maintainer silently pushes a fix, but before any CVE or advisory is published. They are invisible to every scanner that relies on CVE feeds. Attackers can reverse-engineer the fix and begin exploiting unpatched systems immediately. Defenders have no signal, no patch notice, and no indication of exposure. VulNow detects these vulnerabilities in the pre-disclosure window and surfaces them as PreCVEs.

⦹

Vuln Identified

Maintainer discovers security-relevant bug in dependency

✓

Silent Patch Committed

Fix pushed to repo. No CVE filed, no advisory issued

▲

Releases Unprotected

Prior versions remain vulnerable. CVE scanners show all-clear.

◈

Threat Actor Window

Attacker reverse-engineers patch, scans for exposed systems

✦

CVE Published

Defenders finally receive signal, often weeks or months later

40d

CVE records take an average of 40 days to publish after ID assignment. 80% of exploits are published before the corresponding CVE is officially released (Unit 42, 2024).

15m
Attacker scan start after CVE announcement
12h
Avg time defenders identify exposed systems
5d
Mean time to exploitation in 2025 (Mandiant)
16d
Avg time to patch a critical vulnerability

A 16-day patching window against a 5-day exploitation window is not a security posture. VulNow moves the signal before the chasm begins.

Q3 2026 Production Data

Before the Advisory, Before the Exploit

VulNow flagged 1,294 open source vulnerabilities before they were publicly disclosed in Q3 2026. Four were later exploited in the wild, and VulNow flagged each one before its advisory was published and before it was listed as exploited.

CVEProjectAhead of DisclosureAhead of KEV Listing
CVE-2026-87902WordPress2 hours3 days (CISA KEV)
CVE-2026-89013Dolibarr5 days11 days (VulnCheck KEV)also reproduced by VulNow
CVE-2026-19478GitLab14 minutes2 days (VulnCheck KEV)
CVE-2026-66066Rails1 day27 days (VulnCheck KEV)

With five cases from earlier in 2026 (V8 twice, Apache ActiveMQ twice, and Starlette), nine VulNow findings had been flagged before disclosure and later exploited in the wild by the end of Q3, and more have been listed since. KEV catalogs record exploitation that has already been observed: they are confirmation, not warning.

See every predicted KEV →
81%
Flagged more than a full day before any public advisory
of 1,864 confirmed PreCVEs
53%
Flagged more than a week ahead
of 1,864 confirmed PreCVEs
4.8%
False-positive rate across analyzed findings
225 of 4,674 analyzed findings

Figures as of September 30, 2026. The false-positive rate covers findings that have reached an outcome (about 11% of all findings at quarter end). As of late October 2026, more than 3,000 VulNow findings have been confirmed by a published security advisory.

View the full confirmed dataset →
Download Full Q3 2026 Report (PDF, 556 KB)
Why CVE Feeds Are Not Enough

The Numbers Behind the Blind Spot

80%

Exploits precede CVE publication

80% of exploits are published before the corresponding CVE is officially released, with an average lead of 23 days (Unit 42, State of Exploit Development, 2024).

2–27d

Exploitation listings trail the signal

In every Q3 2026 case where a VulNow finding was later exploited in the wild, the KEV listing most programs use to escalate trailed VulNow's detection by 2 to 27 days. KEV catalogs record exploitation already observed: confirmation, not warning.

EU Cyber Resilience Act
✓ CRA-Ready Intelligence

PreCVE Intelligence Meets EU Regulatory Reality

The EU Cyber Resilience Act mandates that manufacturers of products with digital elements actively identify, document, and address vulnerabilities, including those not yet publicly disclosed. CVE-based tooling alone cannot satisfy this requirement.

VulNow's PreCVE intelligence directly addresses the CRA's requirements for proactive vulnerability handling, giving EU-regulated organizations a defensible, documented advantage over the silent fix window.

CRA reporting obligations became applicable on September 11, 2026, and the rest of the regulation applies from December 11, 2027. Organizations that have not established proactive vulnerability intelligence programs are already behind.

◆

The 24-Hour Clock Is Live

Since September 11, 2026, manufacturers must send an early warning within 24 hours of becoming aware of an actively exploited vulnerability, a notification within 72 hours, and a final report within 14 days of a corrective measure. In every Q3 exploited case, VulNow had identified the component, affected versions, and fixing change before the advisory existed. Summary of public guidance, not legal advice.

▲

Proactive Vulnerability Identification

CRA Article 13 requires manufacturers to identify and document vulnerabilities including those discovered before public disclosure. PreCVEs satisfy this before the CVE exists.

◈

SBOM Hypercare

CRA mandates software bill of materials transparency. VulNow enriches your SBOM data with real-time PreCVE risk signals your components carry before any CVE exists.

✦

Distribution-Weighted Severity for Regulated Environments

Standard CVE scoring underweights distribution scale. VulNow's severity is refined against real-world download and deployment data (Tier 2 plan), providing defensible risk classification for regulated product portfolios.

Two Ways to Use VulNow

Defend Your Stack, or Embed PreCVE in Your Product

Whether you're protecting your own software supply chain or shipping next-generation security tooling, PreCVE intelligence opens new categories of detection.

For CISOs, AppSec leads & product security teams

Defend Your Software Supply Chain

  • PreCVE alerts for your active dependencies before public disclosure
  • Prioritize remediation before CVE noise and alert fatigue begins
  • Reduce exposure window on foundational packages like react, axios, django
  • Severity calibrated to your real download exposure, not generic CVSS
  • Shift from reactive triage to proactive patching with a measurable lead time advantage
Start Predictive Pilot Program
See intelligence tiers →
Intelligence & Research

From the VulNow Team

Original research on software supply chain risk, PreCVE intelligence, and the data behind modern vulnerability management.

October 28, 2026

The Starlette Case: Flagged 103 Days Before CISA Listed It as Exploited

VulNow flagged a Starlette authentication bypass on May 22. CISA added it to its KEV catalog on September 2, after exploitation was tied to Qilin ransomware actors.

Read article ›
October 25, 2026

VulNow Q3 2026 Report: Before the Advisory, Before the Exploit

1,864 confirmed PreCVEs, four exploited-in-the-wild vulnerabilities flagged before their advisories and exploitation listings, and what EU CRA reporting means for lead time.

Read article ›
August 2, 2026

VulNow Q2 2026 Report: The Disclosure Gap, Measured

320+ confirmed PreCVE detections, a disclosure system that has publicly said it can't keep up, and VulNow's appointment as a CVE Numbering Authority.

Read article ›
June 30, 2026

VulNow Becomes a CVE Numbering Authority under ENISA Root

VulNow B.V. today announced its formal appointment as a CVE Numbering Authority (CNA) under the ENISA CVE Root, authorizing the company to directly assign CVE identifiers to vulnerabilities surfaced by its predictive intelligence engine.

Read article ›
April 15, 2026

VulNow Q1 2026: 58 PreCVE Detections Confirmed

First full quarter of production PreCVE intelligence: 58 verified detections across 28 packages and 13.2 billion monthly downloads, with average lead time of 6.6 days.

Read article ›
April 2, 2026

The $60 Billion Problem Nobody's Fixing: Why Package Registries Keep Getting Hacked

A data-driven investigation into why 83% of supply chain attacks could have been prevented, and why the solution that already exists remains ignored.

Read article ›
Team

Built by People Who've Lived This Problem
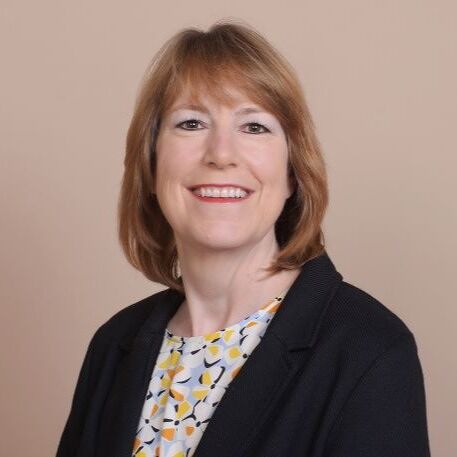
Cassie Crossley

Cassie Crossley

CEO & Co-Founder

Author of Software Supply Chain Security (O'Reilly). Former VP of Supply Chain Security at Schneider Electric (a €38B global enterprise), where she led product security and cyber resilience programs across complex international supply chains. Internationally recognized speaker and authority on vulnerability management, product risk, and EU regulatory compliance. Board director at Cybeats.
O'Reilly Author30+ years security leadershipSchneider Electric VPEU CRA expertiseQTE designation
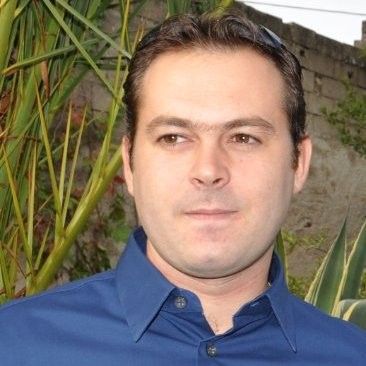
Valerio Mulas

Valerio Mulas

CTO & Co-Founder

20+ years in security, cloud architecture, DevOps, and resilient infrastructure across regulated and mission-critical environments. Built and secured large-scale production systems in Banking and Fintech using AWS, Kubernetes, IaC, and CI/CD automation. Leads VulNow's technical platform, translating deep engineering expertise into scalable predictive vulnerability intelligence.

20+ years security engineeringCloud architectureDevSecOpsBanking & Fintech
Predictive Pilot Program

Don't Wait for the CVE.
Get the Signal First.

Join VulNow's Predictive Pilot Program. Receive live PreCVE detections for your dependency stack, or integrate our intelligence feed into your security platform.

Contact: info@vul.now · Netherlands-based · Serving most global markets